LNbits 1.7.0rc4 reaches PyPI: a test package is not a stable-service all-clear
Source report: 2026-11-10 · Editorial analysis published: 2026-11-10
The November 10 package follows security work merged on November 9. PyPI marks it as a prerelease; GitHub’s latest published stable release remains a separate check.
A new package is now available to test
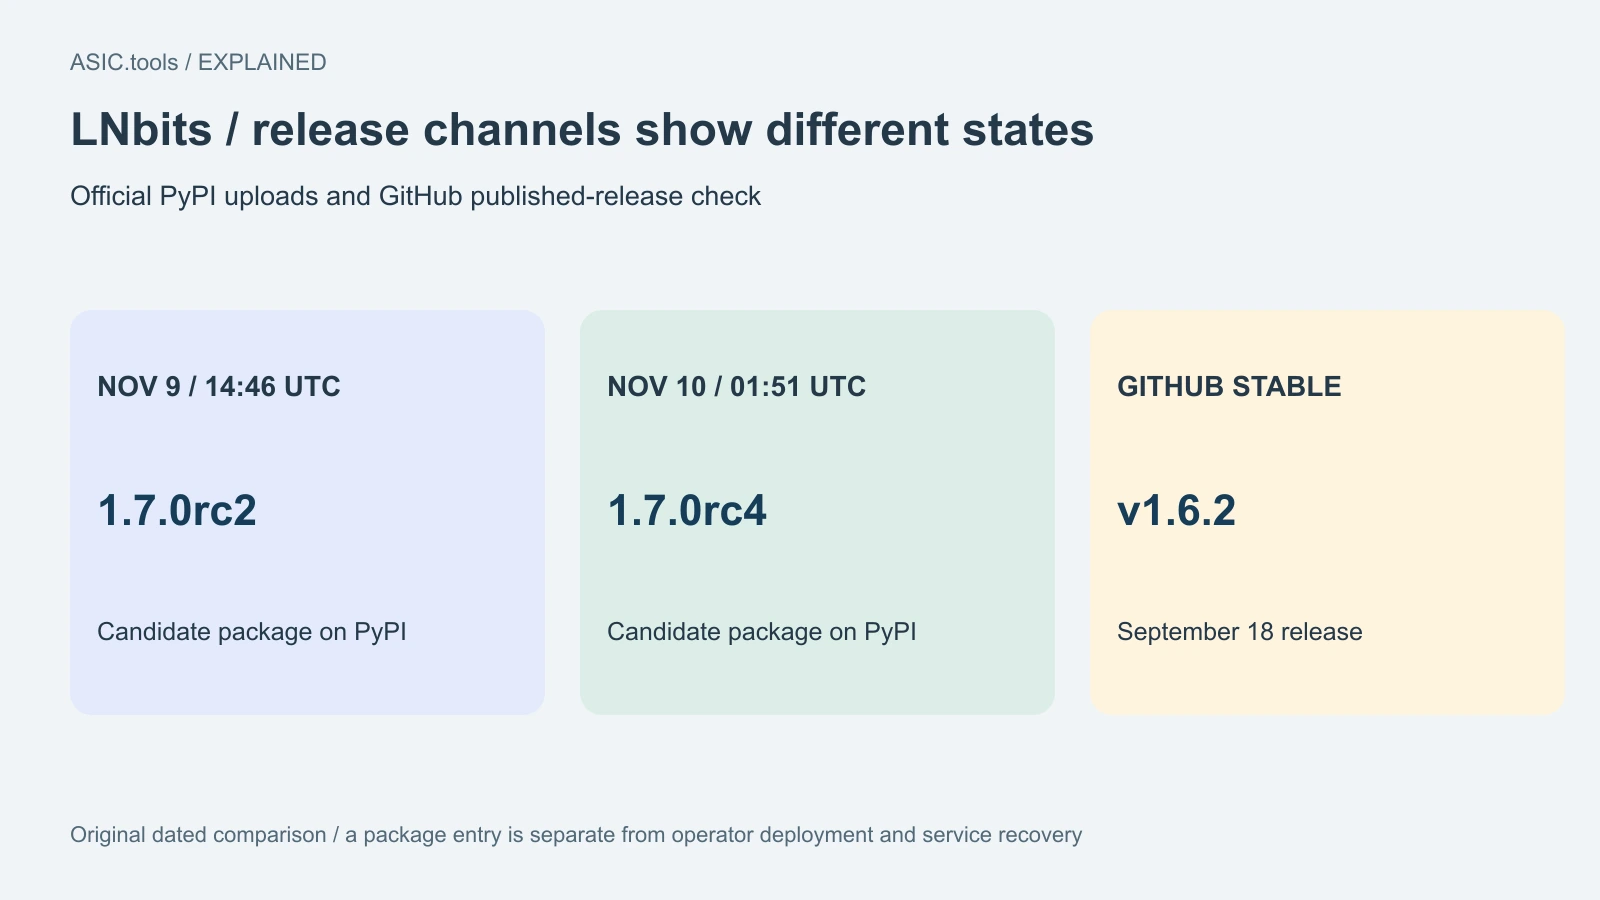
LNbits 1.7.0rc4 was uploaded to the official project’s PyPI package on November 10 at 01:51 UTC. That is a concrete development after the November 8 emergency server-stop warning: operators and developers now have a newly published version to examine. PyPI explicitly labels it a prerelease, which may not be stable for production use. The letters rc mean release candidate, a version still being checked before a normal stable release.
The package follows 1.7.0rc2, uploaded on November 9 at 14:46 UTC. LNbits also merged security changes numbered 4310 and 4313 on November 9. These are separate evidence points: a change entering the source repository, a package being published and a particular service becoming available to its users are not the same event. The new package alone does not confirm that every affected installation has recovered.
Check which version list you are reading
At our November 10 check, GitHub’s latest published stable release was still v1.6.2, dated September 18. That release describes a PostgreSQL backup hotfix. Its position as latest in the GitHub releases list does not turn it into a newly issued patch for the November incident. Conversely, seeing 1.7.0rc4 on PyPI does not mean GitHub has announced a normal stable 1.7.0 release.
The distinction matters because operators obtain LNbits through different installation methods. A package version available in one channel is not proof that another channel or a hosted service has changed. Read the exact version and prerelease status, rather than relying on a generic stable badge or a page’s position in search results. A service operator’s deployed version is an additional fact that must be checked for that service.
What the security work changes
The merged source changes centralize checks on outbound requests and tighten protection against a server being directed back at itself or into private destinations. This class of problem is called server-side request forgery, or SSRF: an application can be persuaded to make a request on someone else’s behalf. The change titles and source history establish work on those protections; they are not a complete forensic account of every attack reported during the incident.
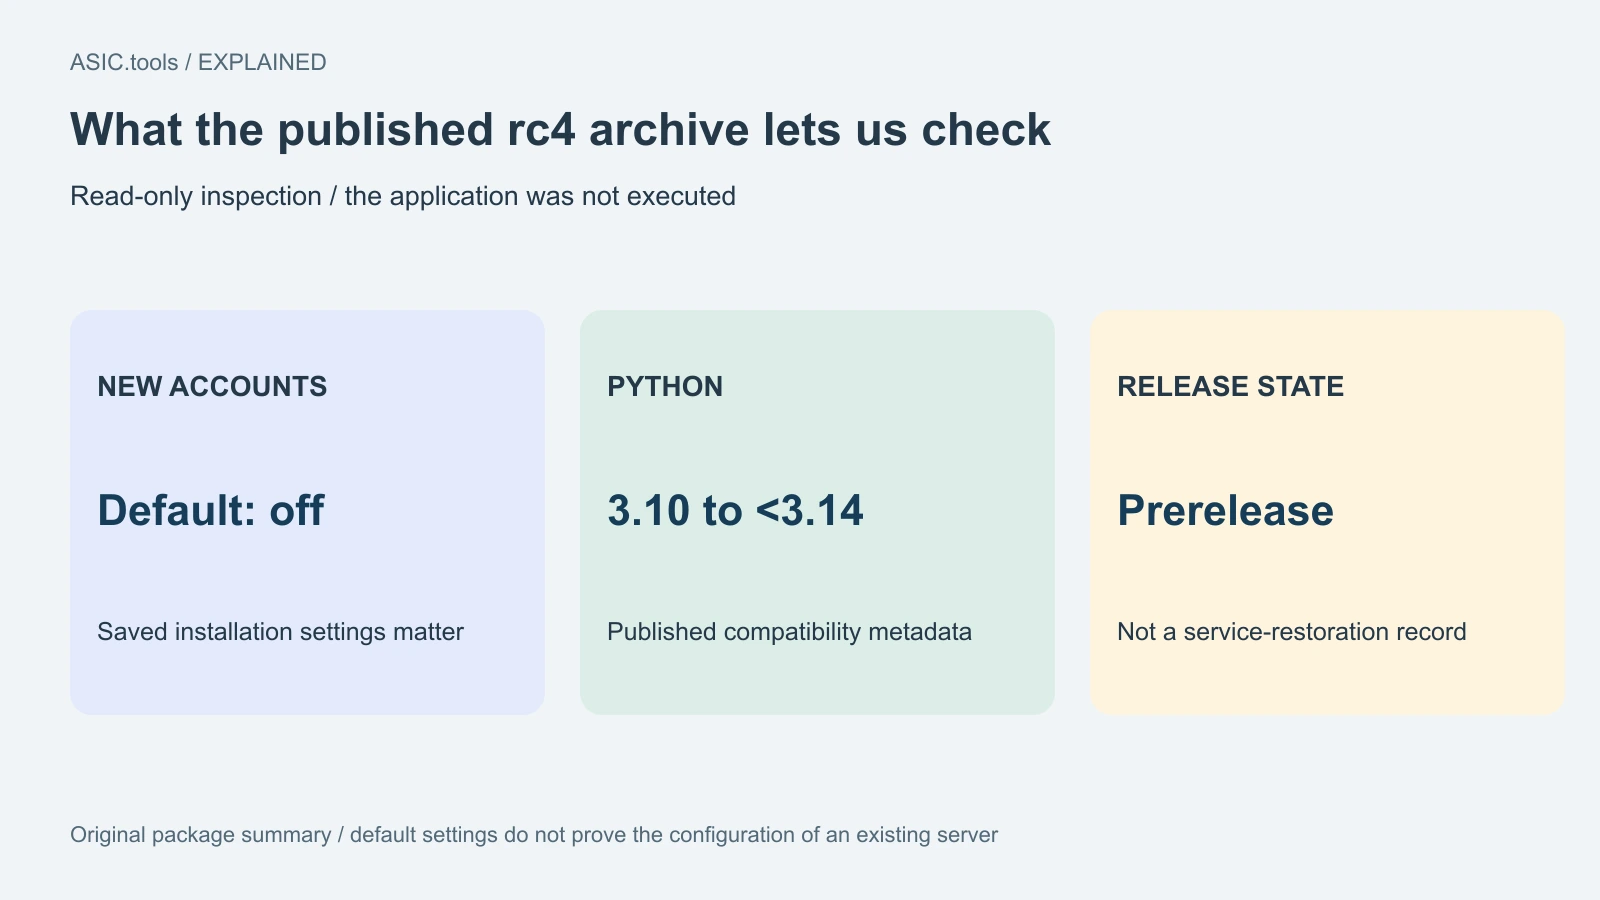
We also inspected the published rc4 source archive without running the software. Its default setting for allowing new accounts is false, and its package metadata requires Python at least 3.10 and below 3.14. A default in new code does not prove that an existing installation’s saved configuration has the same value. Operators still need to understand the configuration they actually deploy and the compatibility of their own installation.
Why a miner may care about a wallet application
LNbits is a Bitcoin and Lightning application layer, not the Bitcoin consensus protocol or an ASIC’s mining firmware. The news matters to a miner when the actual payout or receiving arrangement uses LNbits. It does not mean every Bitcoin miner needs to install this package, change pools or replace an ordinary on-chain receiving wallet that does not use LNbits.
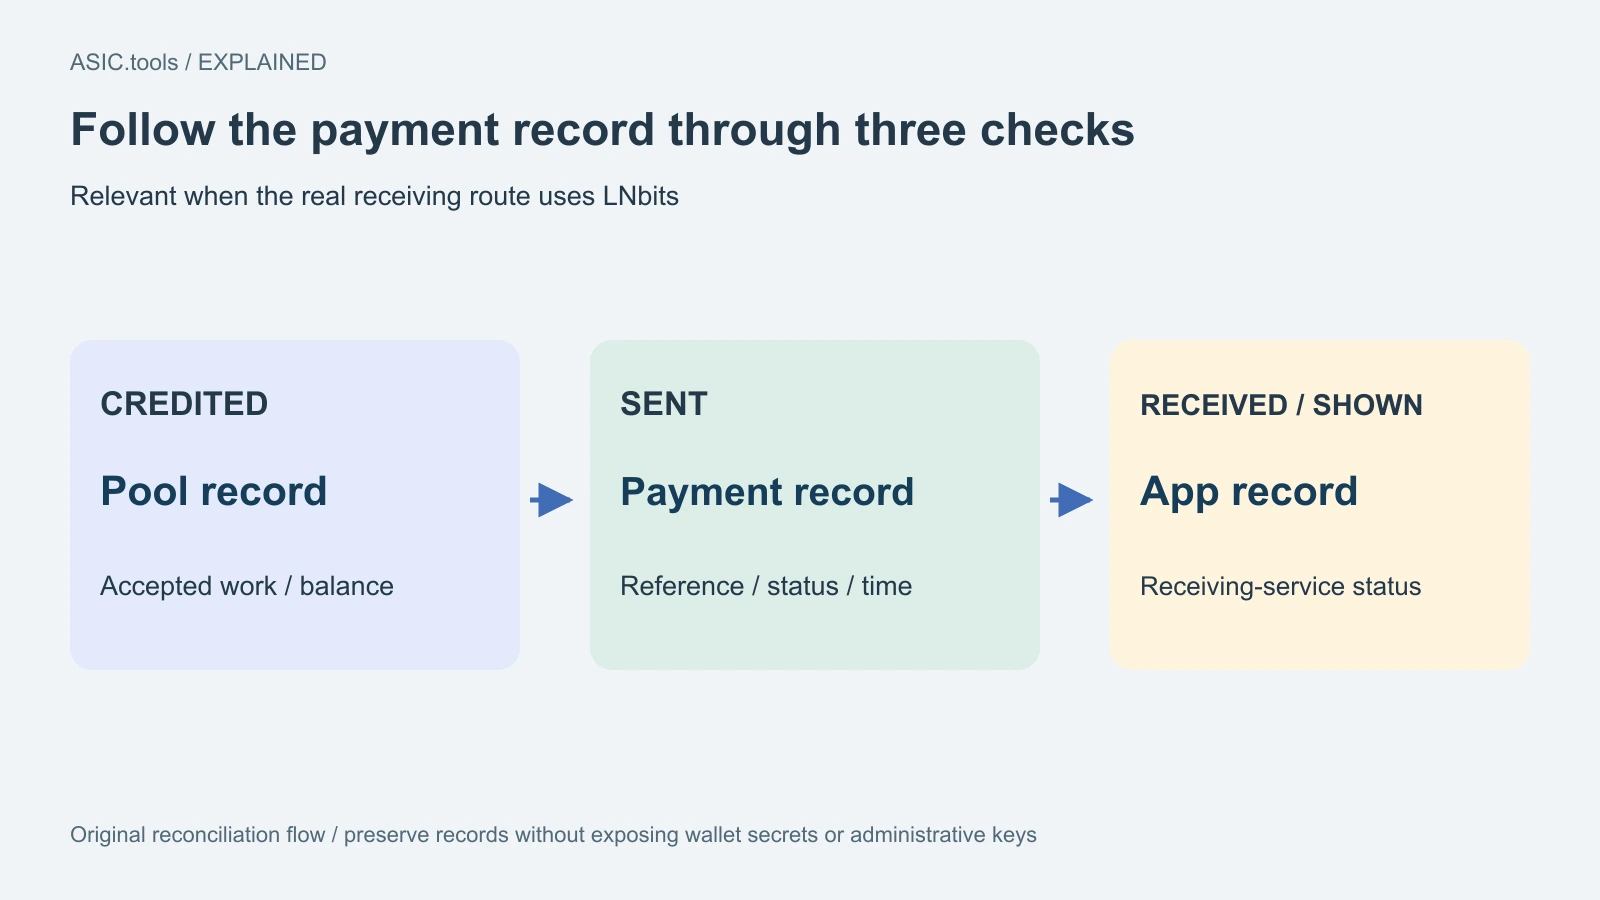
Separate the stages when investigating a payment: did the mining pool credit the work, did it send a payment, and can the receiving application account for and display it? A working miner cannot by itself establish that the receiving service is healthy. Equally, a receiving-service interruption does not automatically mean that the ASIC stopped submitting accepted work. Keep the relevant pool and payment records before drawing a conclusion.
A useful question for the operator
For a hosted LNbits account, ask the service operator which exact version is deployed and what guidance applies to that service’s recovery. A public package upload timestamp cannot answer that on behalf of the operator. For a self-hosted installation, keep the package version, installation method, configuration and backup information together so that testing or restoration has a clear starting point.
Do not publish wallet secrets or administrative keys when asking for help. A payment reference, status and time can be kept as part of the investigation without exposing the credentials that control money. The aim is to reconcile what happened to the actual payment route, not to assume that a new version number has already repaired every account or returned any previously missing funds.
Progress, with a clearly named release state
The fresh development is that rc4 is available as a dated test package, alongside visible security changes in the project’s source. Testing a candidate in an isolated setup can provide information about compatibility, but it is different from declaring a money-handling service ready to reopen. This report did not run LNbits, test an exploit or independently certify the package as safe.
Read current official project instructions and the operator’s own service notice before treating the incident as resolved for a particular installation. A merged fix, a published release candidate, a deployed update and a working customer service are distinct milestones. Keeping those labels accurate lets miners follow actual recovery progress without mistaking a package catalogue entry for confirmation that their own receiving service is back.
Source: LNbits / PyPI and official source ↗ · Official GitHub releases ↗ · Merged security change 4310 ↗ · Merged security change 4313 ↗ · Versioned PyPI metadata ↗
Mining calculator ↗